
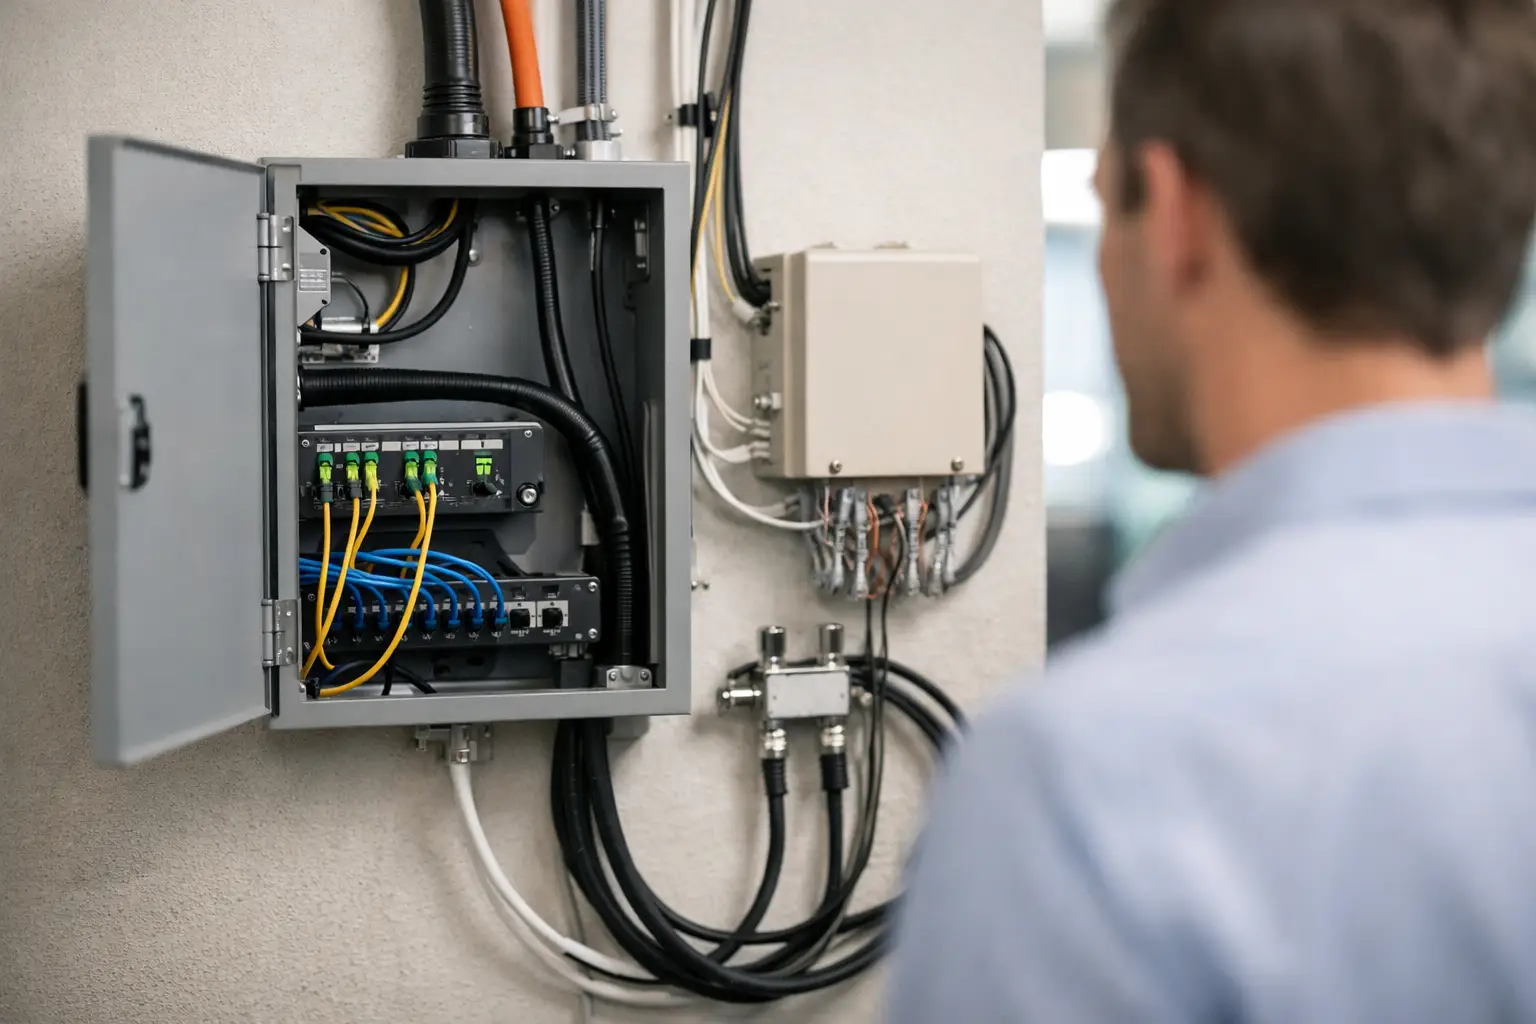
A circuit is down. The carrier says its service is healthy. Your IT team sees no signal past the telecom room. Facilities has a locked closet, an outside plant contractor is involved, and no one can identify the last tested handoff. That is when a basic question becomes an operational problem: what is a demarcation point?
A demarcation point is the defined boundary where one party's communications service or infrastructure responsibility ends and another party's begins. In a commercial building, it most often marks the handoff between a service provider's network and the building owner's, tenant's, or enterprise's internal network.
The concept is simple. The consequences of getting it wrong are not. A vague demarcation can turn a straightforward outage into hours of vendor handoffs, disputed responsibility, and avoidable tenant disruption.
What Is a Demarcation Point and Why Does It Matter?
In telecommunications, the demarcation point, often shortened to demarc, establishes where a carrier delivers service and where the customer environment begins. It may be a network interface device, an optical network terminal, a fiber patch panel, a smart jack, or another clearly identified physical connection. The exact device depends on the service type and the facility.
For a traditional copper service, the point may be a provider-owned interface mounted near the building entrance. For fiber internet, it may be an optical handoff in a main telecom room. For a modern Ethernet circuit, the carrier may provide a managed device that presents a copper or fiber port for the customer's firewall, router, or switch.
The physical location is only part of the definition. A useful demarcation point also identifies four things: the responsible party on each side, the interface presented, the service performance expected at that interface, and the process for testing a fault.
Without those details, a demarc is just a box or patch panel with a label. With them, it becomes an accountability boundary.
The Demarc Is Not Always the Building Entrance
A common assumption is that the demarcation point sits wherever a carrier's cable enters the property. Sometimes it does. Often, it does not.
A service provider may bring fiber into a building entrance facility, extend it through conduit or riser pathways, and terminate it in a main distribution frame or telecom room. The contractual service handoff may be at the provider's equipment in that room, not at the exterior wall. In a multi-tenant property, the provider may stop at a shared point of entry while a separate party owns the pathway, riser, and extension to the tenant suite.
That difference matters during an outage. If the service provider is responsible only to a handoff in the basement and the tenant's firewall is on the 18th floor, the building's internal cabling between those locations must have a named owner, current records, and a support path. Otherwise, the gap between the provider and the tenant becomes everyone else's problem.
The same issue appears in campuses, warehouses, medical offices, and mixed-use properties. A circuit can be live at the carrier demarc while the operational service remains unavailable because of a failed internal fiber pair, a damaged patch cord, an unpowered media converter, or an undocumented cross-connect.
Demarcation Point vs. Network Boundary
The demarcation point is a responsibility handoff. The network boundary is a security and operational control boundary. They may be close together, but they are not the same thing.
For example, a carrier may deliver Ethernet to a managed handoff device. From there, a patch cable may connect to an enterprise firewall. The carrier owns and monitors its network up to the delivered interface. The organization owns the firewall policy, internal routing, wireless environment, segmentation, and user access beyond it.
Confusion starts when teams treat the provider handoff as proof that the business is protected or operational. A carrier can verify light levels, link status, and service delivery at the demarc. That does not confirm that a firewall is configured correctly, a switch port is enabled, a UPS is healthy, or building systems have an available path to the services they need.
For facilities with access control, cameras, building automation, elevators, life safety integrations, or tenant connectivity, this distinction deserves special attention. The network may cross several ownership boundaries before it reaches the device that matters. Every one of those boundaries needs a documented standard.
What a Defensible Demarcation Record Includes
The most effective demarcation documentation is built for the person responding at 2 a.m., not just for a project closeout binder. It should let an IT manager, facilities director, or service technician quickly establish what is delivered, where it is delivered, and who owns the next action.
At minimum, maintain these four records for every production circuit:
- A precise location: building, floor, room, rack, cabinet, panel, and port identification. “Basement telecom room” is not precise enough when a property has multiple locked spaces.
- A physical and logical description: carrier circuit identifier, service type, handoff medium, connector type, interface speed, addressing method where applicable, and the equipment connected on the customer side.
- An ownership map: the provider's responsibility, the property-side responsibility, the tenant or enterprise responsibility, and any managed-party role. Include after-hours escalation contacts and access requirements.
- Test and restoration information: the approved test point, baseline readings or performance expectations, power dependencies, backup-path details, and the last date the handoff was validated.
Photographs help, especially when they show labels, rack position, patching, and nearby power equipment. They do not replace records. A photo can show where a cable was on the day it was taken; it cannot establish whether that cable is still the active path, whether it was tested, or whether the provider accepts that point as its service boundary.
Design the Handoff Before Construction Ends
Demarcation failures are frequently created during construction and renovation, then discovered during occupancy. The project team orders service, the carrier installs equipment, a low-voltage contractor extends cabling, and the tenant's IT equipment arrives later. Each party completes a portion of the work. No one confirms the end-to-end path under operating conditions.
The result is a handoff that looks complete but lacks acceptance. Labels may be inconsistent. The circuit may be terminated in a room without controlled access. The customer-side fiber may be too short, untested, or routed through a pathway with no spare capacity. Equipment may rely on convenience power rather than conditioned, backed-up power.
Final acceptance should include a witnessed service test from the provider handoff through the customer edge equipment. For critical sites, test the primary and secondary paths separately, including failover behavior. Confirm that the documented circuit identifier matches the provider's records and that the physical labels match the drawings and inventory.
This is not paperwork for its own sake. It is how the organization proves that a circuit was delivered to the agreed point and that the infrastructure beyond that point can support the intended service.
Ownership Gaps Create Longer Outages
A demarcation point is where fragmented delivery becomes visible. The carrier may own the incoming service. A construction team may have installed the backbone cabling. Facilities may control room access and power. IT may operate the firewall and switches. A security team may rely on the connection for remote camera access. If those groups operate independently, a small fault can become a long outage.
The practical answer is not to make every team responsible for everything. It is to establish one operating standard and one accountable process for the whole service path.
That process should define who opens a carrier ticket, who grants room access, who can authorize changes to cross-connects, who validates restoration, and who updates the records afterward. It should also make clear who owns the internal extension from the demarc to the network edge. “The carrier says it is good” is not a restoration standard for the business.
For managed properties, this governance model should be repeated across the portfolio. A consistent demarcation standard reduces the time spent rediscovering each building's layout during an incident and makes vendor oversight measurable rather than informal.
Common Demarcation Point Mistakes
The most damaging mistakes are usually ordinary ones. The demarc is unlabeled, or labeled only with a carrier name that changes over time. The service handoff is in a locked room but the escalation team has no access procedure. A provider-managed device is powered from an unprotected outlet. The circuit inventory lists a suite number but not the rack, port, or customer-side equipment.
Another common problem is treating an old drawing as operational truth. Buildings change. Telecom rooms are renovated, racks are replaced, tenants expand, and patching moves. A demarcation record must be updated after moves, adds, changes, and incident repairs. If the documentation is not part of the change process, it will eventually become unreliable.
Redundancy can introduce its own false confidence. Two circuits are not truly diverse if they enter through the same conduit, terminate in the same room, depend on the same power source, or share the same internal fiber pathway. The demarcation points for primary and backup service should be reviewed as part of the full resilience design, not as isolated carrier details.
Make the Demarc an Operating Control
The right question is not merely where the provider stops. Ask where your organization can test service, where responsibility changes, and who is accountable for restoring the complete path that supports operations.
Walk each critical circuit during normal business conditions. Verify its physical handoff, labels, room access, power source, internal extension, customer-edge connection, and escalation path. Then test the records during a planned exercise, when there is time to correct ambiguity rather than argue about it during downtime.
A well-managed demarcation point does not prevent every outage. It does prevent a preventable failure of ownership when the building needs clear answers most.